The intelligence bridge between America and Asia.
We help US security and intelligence teams model their Asia footprint with AI, watch the adversaries targeting it upstream, and verify whether they’re exposed.
Request a 4-week proof-of-concept
One live use case, run end to end.
- 17,000 comments in Singlish, Mandarin and Chinese dialects, narrowed to 11 malicious profiles within 8 hours.
- A silent fix in an open-source AI gateway would have been flagged ~7 months before CVE scanners saw it, in a backtest on public data.
- One real incident found among ~1,000,000 log rows, confirmed by a sectoral CISO.
Asia remains a key supply chain hub for the world.
Engineers in India, vendors in China, contact centers in the Philippines. Adversaries reach you through them, in places and cultures your tools don’t read.
Local service offices, engineering functions, manufacturing assets and suppliers. What’s your exposure in Asia?
We’re seeing a growing number of regional incidents that materially impact global businesses.
- CoinbaseBribed outsourced agentsUS$307M in breach costs
- QantasSocially engineered contact center5.7M customers’ data exposed
- StellantisBreached vendor platformCustomer contact data exposed
Public incidents. None is a Protos Labs customer.
See what West-centric feeds miss.
The threat signals targeting your staff, vendors and software in Asia, interpreted with local cultural context and drawn from restricted-access datasets.
Nation-state intelligence tradecraft
We’re cyber operators with national-security backgrounds, proven on national missions with defense and homeland-security agencies since 2024.
Asian cultural context
Firsthand understanding of the region’s cultural nuance, so we see what US-based teams can’t.
Multi-source data fusion
We ingest and analyze datasets across cyber and influence operations to identify early adversarial signs. For instance, LinkedIn recruitment of remote workers can be an early sign of an attack. We also have first-party access to specific Asian datasets.
Around the clock
Our Asia-based operators work while the US sleeps, so findings are ready when your working day starts.
The people you’ll work with.
Joel Lee
Co-founder & CEO, Singapore
Ex-Booz Allen Hamilton (Cyber Intelligence).
Simeon Tan
Co-founder & CTO, Singapore
Ex-Booz Allen Hamilton (OT Security).
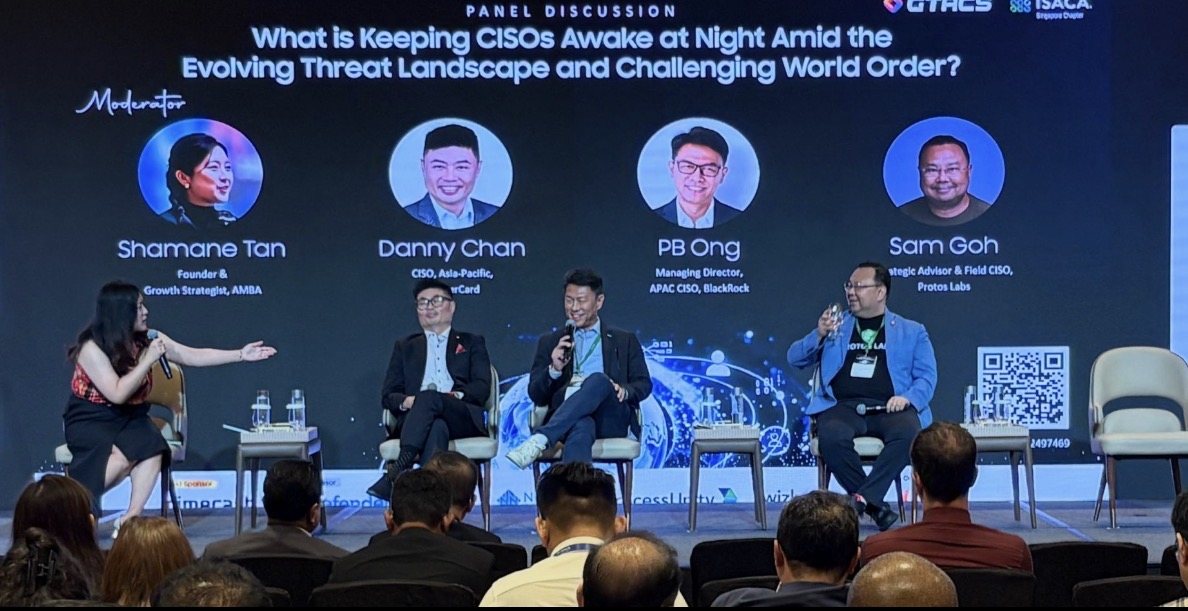
Sam Goh
Field CISO & GM, New York
Previously CISO at Siam Commercial Bank DataX (Data & AI CoE).
sam_goh@protoslabs.io
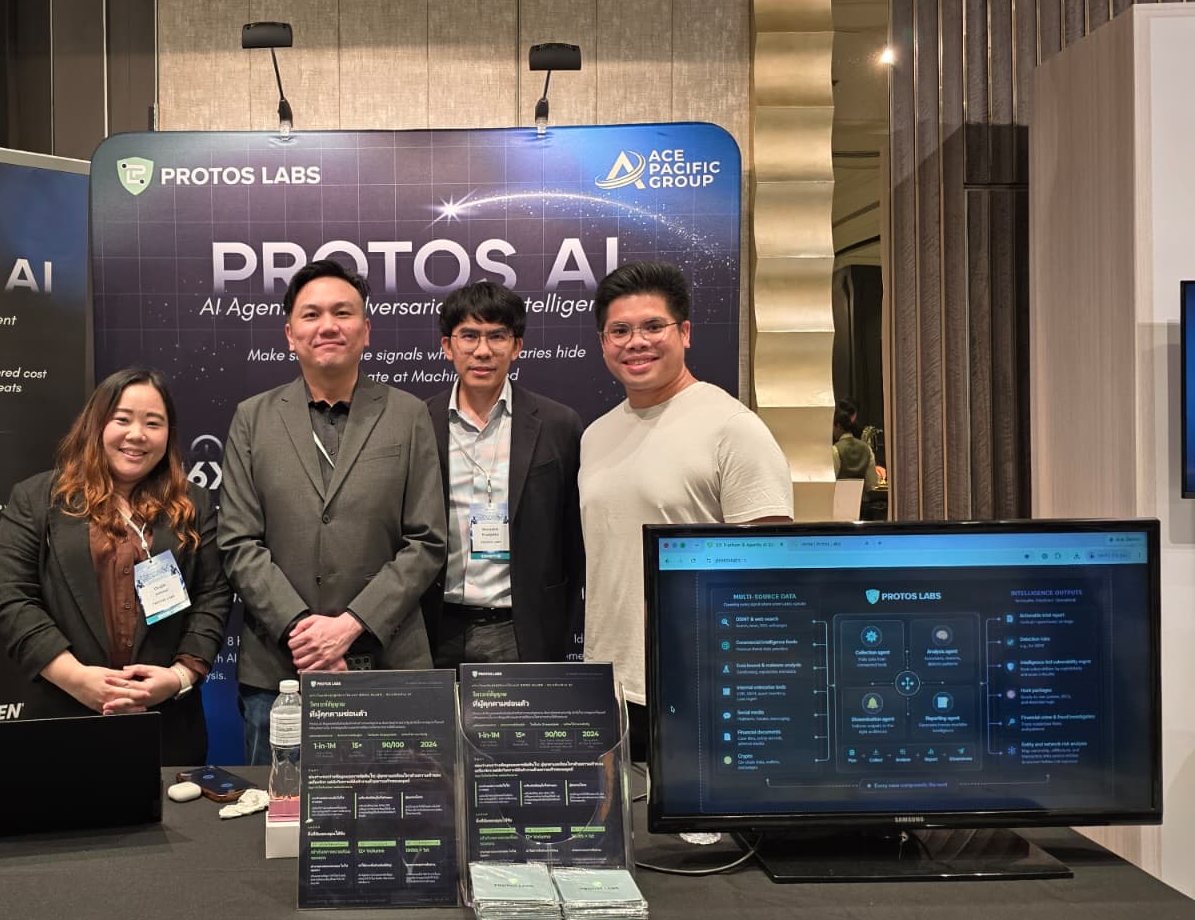
Model. Collect. Analyze. Hunt. Track.
Protos AI models your environment, goes upstream to collect early-warning signals, and carries every finding into a hunt to verify whether you’re exposed. You stay in full control, setting the requirements and approving every conclusion before release.
Understand your environment first.
We model your assets, vendors, software, AI systems and workforce, so collection targets what actually puts you at risk, not generic data from a shared feed.
Intelligence that executes.
We carry every finding into a hunt in your environment, ending in one answer: Are you exposed or not?
Results from live deployments.
Coordinated inauthentic behavior
17,000 comments narrowed to 11 malicious profiles within 8 hours of first prompt.
Homeland-security agency. 6,000 profiles in Singlish, Mandarin and Chinese dialects, analyzed by one analyst with Protos AI, against an estimated 48 analyst-hours (3 analysts × 16 hours).
Retrospective threat hunt
One real incident found among ~1,000,000 log rows, confirmed by a sectoral CISO.
Command-and-control traffic invisible to human analysts, detected by correlating logs across dozens of research and education institutions.
Threat-intelligence analysis
~4 hours of analyst work per threat cut to ~15 minutes.
Critical-infrastructure CTI team.
“In one deployment, Protos AI surfaced a single anomalous event buried in over a million rows of our security logs — and our team confirmed it matched a real incident. That is not something we could have found manually.”
“On national-security missions, Protos AI has changed what our analysts can get through. Investigations that used to take days now take hours, and the conclusions hold up to the scrutiny our work demands.”
In the press.
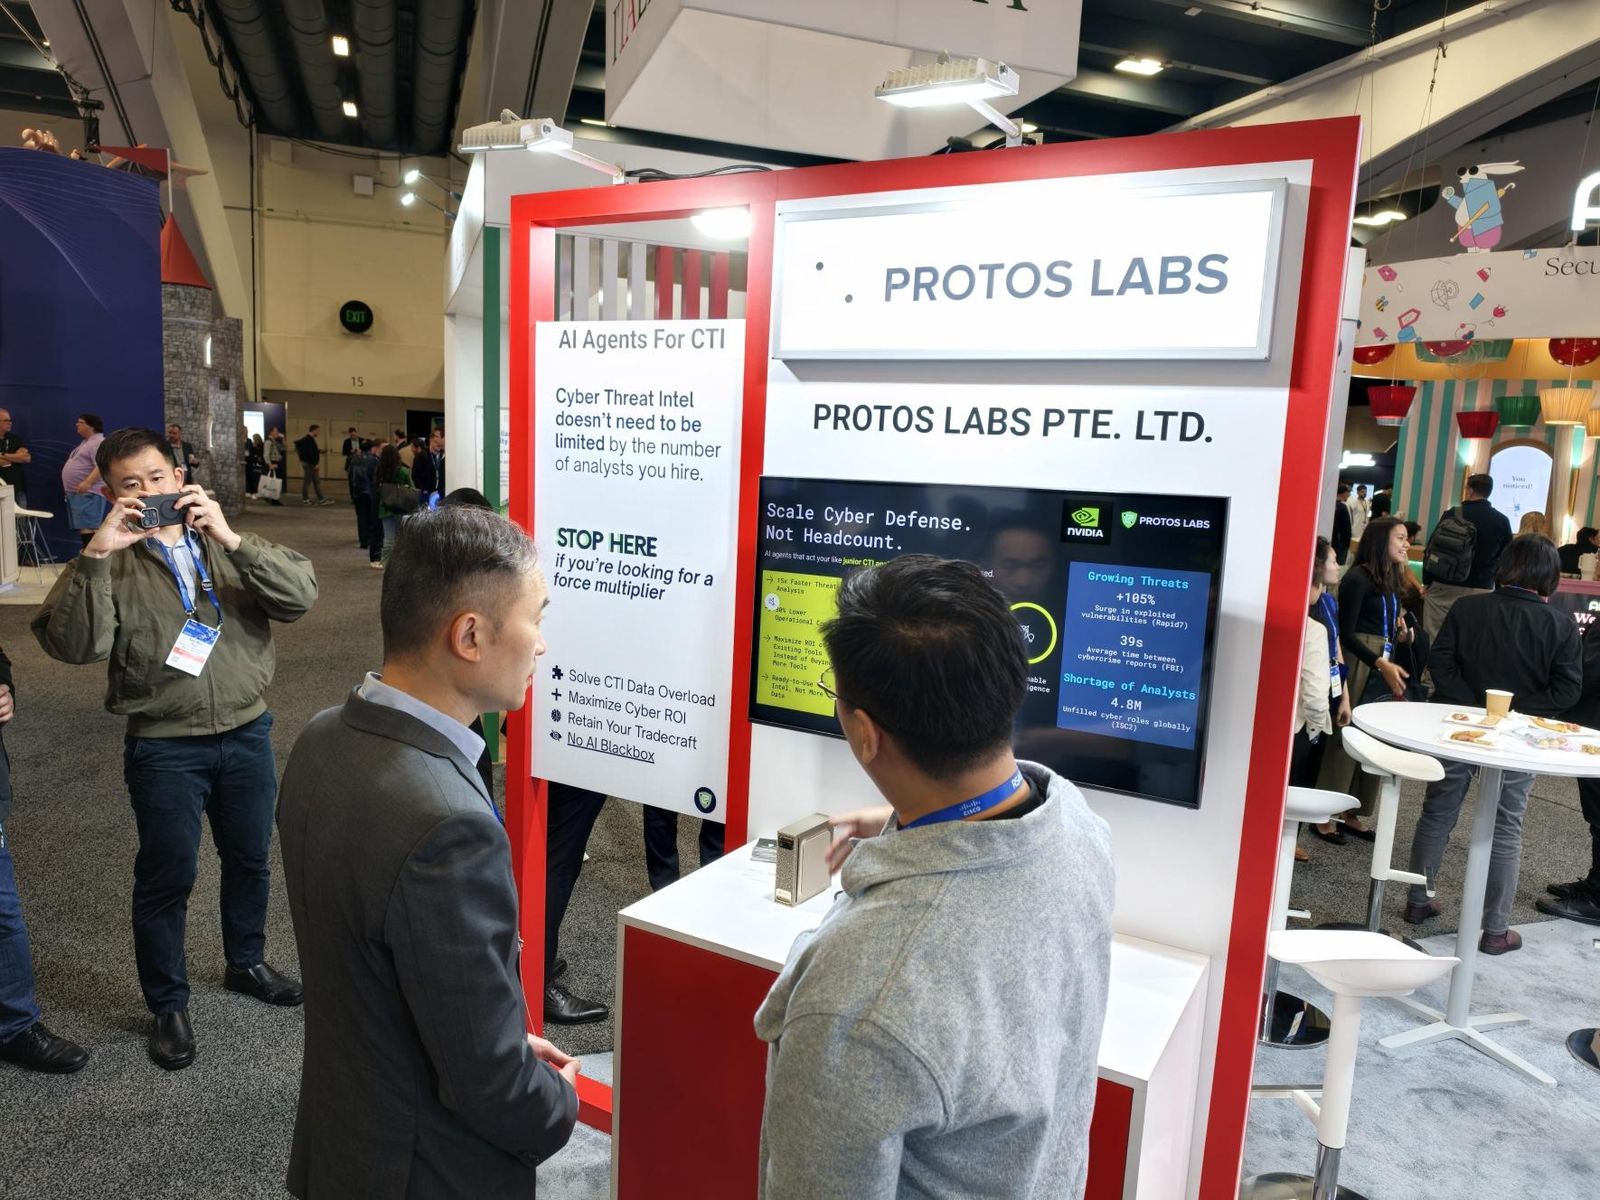
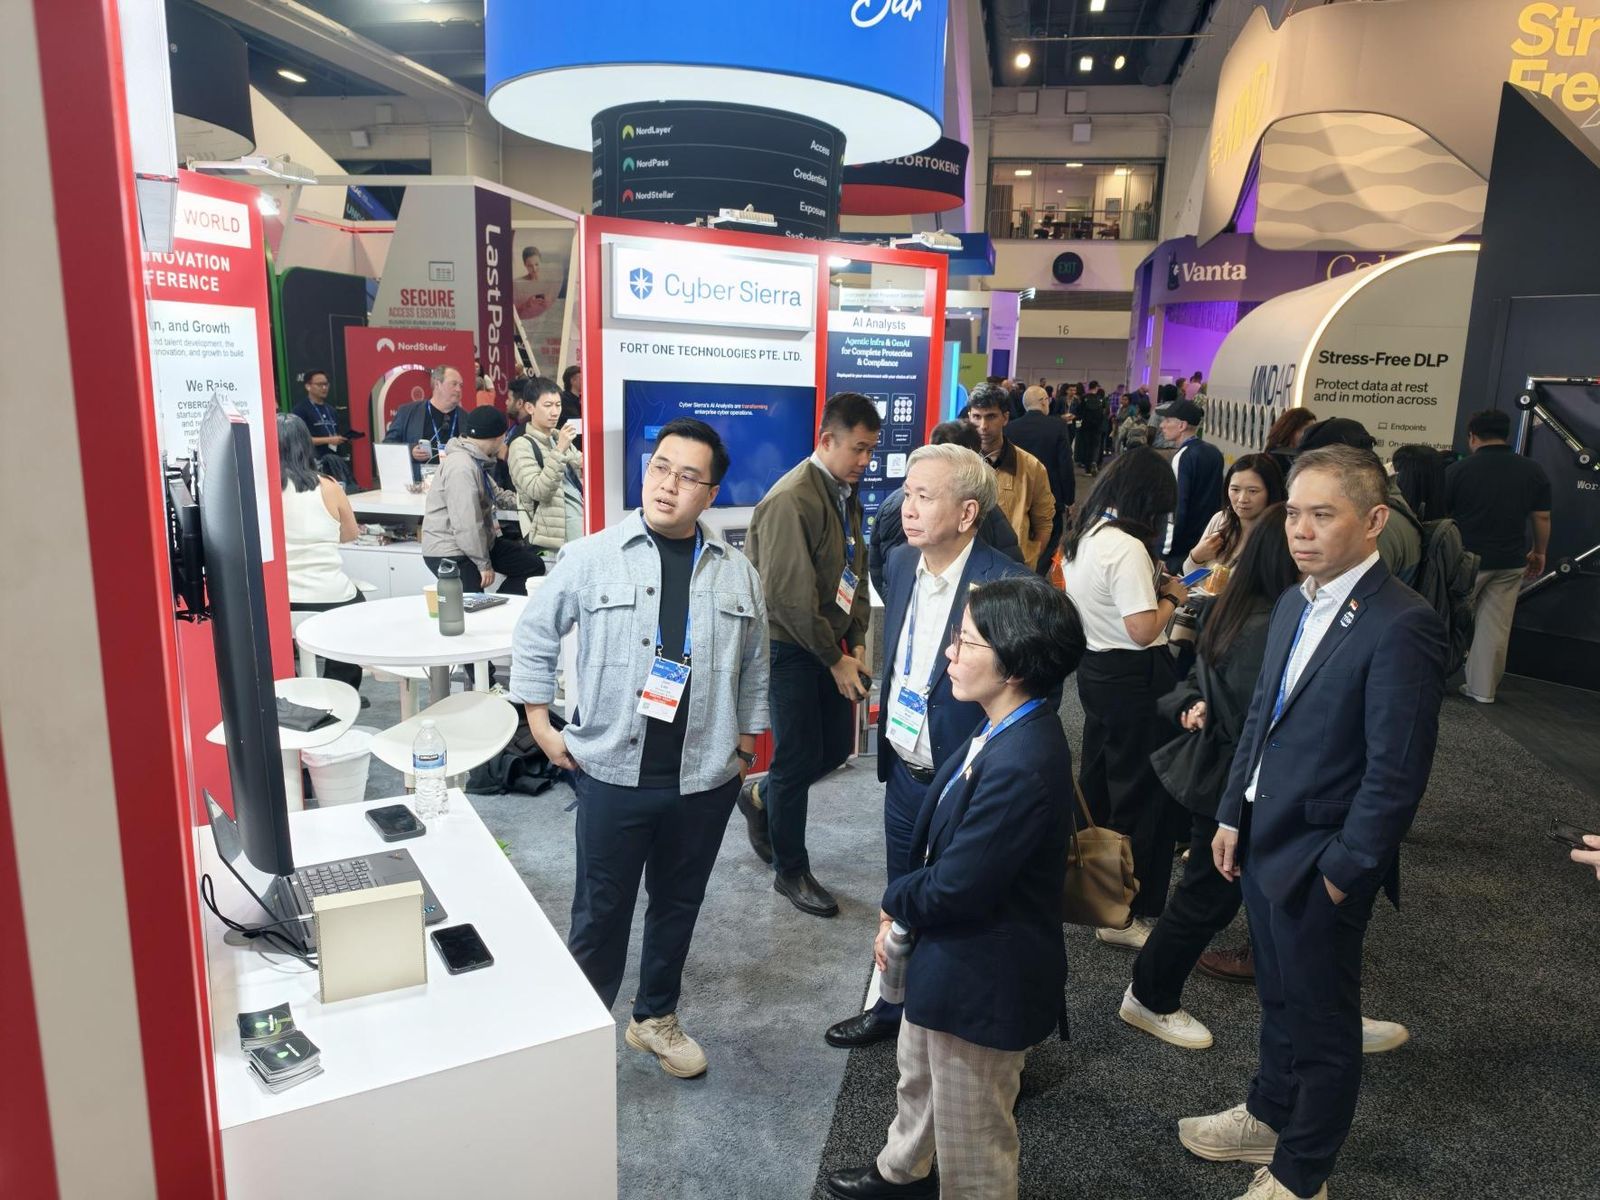
Coverage of the Protos AI launch at RSA Conference 2026 in San Francisco, and since.
- Mar 23, 2026Business WireProtos Labs Launches Freemium Agentic AI Platform for Cyber Threat Intelligence at RSA Conference 2026↗
- Mar 23, 2026Security BoulevardProtos Labs Opens Up Protos AI for Free, Targeting CTI Teams at RSAC 2026↗
- Mar 24, 2026Help Net SecurityProtos AI delivers agent-driven threat intelligence without vendor lock-in↗
- Mar 25, 2026Dark ReadingLeveraging AI Agents: The Protos Labs 3C Framework for Unified Enterprise Risk Intelligence↗
The Business Wire release was also carried by Yahoo Finance.
Built by intelligence operators, proven on national security missions.
Anyone can build an AI agent. Few can build it on nation-state intelligence tradecraft.
Trust you can measure
- Every conclusion traces to its sources and reasoningFull audit logs
- Trust Fabric scores AI output on accuracy, reliability, consistency and speedAt POC and after go-live
Recognition
- CyberCall, Singapore’s national cyber innovation callTwo-time winner
- NVIDIA InceptionMember
- Microsoft AI AccelerateMember
Catch the adversary upstream.
Start with a 4-week proof-of-concept on one live use case. We build every POC on your own workflows, playbooks and data sources, with success criteria agreed with you at kickoff.
Sam Goh, Field CISO & GM · sam_goh@protoslabs.io